Architect | GRC/AI Governance (Remote)
 United States·DallasRemotemid
Quick Summary
Who is Trace3? Trace3 is a leading Transformative IT Authority, providing unique technology solutions and consulting services to our clients. Equipped with elite engineering and dynamic innovation,
Who is Trace3?
Trace3 is a leading Transformative IT Authority, providing unique technology solutions and consulting services to our clients. Equipped with elite engineering and dynamic innovation, we empower IT executives and their organizations to achieve competitive advantage through a process of Integrate, Automate, Innovate.
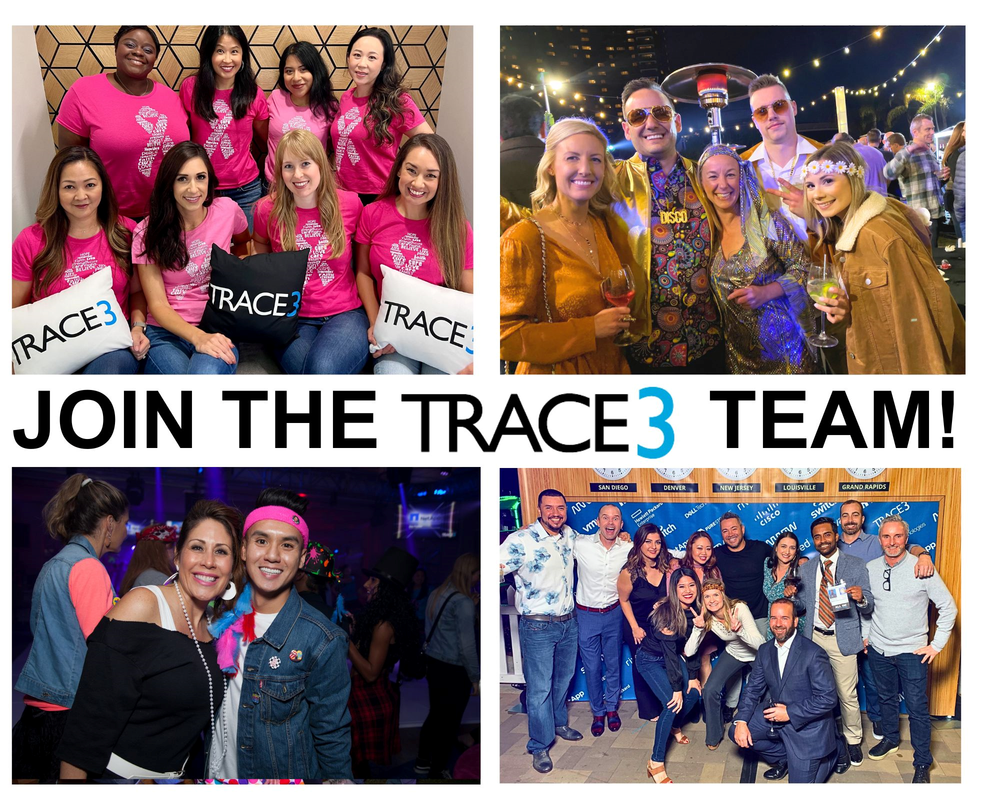
Our culture at Trace3 embodies the spirit of a startup with the advantage of a scalable business. Employees can grow their career and have fun while doing it!
Trace3 is headquartered in Irvine, California. We employ more than 1,200 people all over the United States. Our major field office locations include Denver, Indianapolis, Grand Rapids, Lexington, Los Angeles, Louisville, Texas, San Francisco.
We are flexible and resilient in a fast-changing environment. We continuously innovate and drive constructive change while keeping a focus on the “big picture.” We exercise sound business judgment in making high-quality decisions in a timely and cost-effective manner. We are highly creative and can dig deep within ourselves to find positive solutions to different problems.
We get things done and drive results. We lead without a title, empowering others through a can-do attitude. We look forward to the goal, mentally mapping out every checkpoint on the pathway to success, and visualizing what the final destination looks and feels like.
We are humble individuals who understand how our job impacts the company's mission. We treat others with respect, admit mistakes, give credit where it’s due and demonstrate transparency. We “bring the weather” by exhibiting positive leadership and solution-focused thinking. We hug people in their trials, struggles, and failures – not just their success. We appreciate the individuality of the people around us.
The Architect, Governance, Risk & Compliance (GRC) is a senior, delivery-focused consultant responsible for leading and executing GRC engagements for Trace3 clients. This role performs framework-based security program assessments, risk assessments, and business impact analyses, and translates findings into practical, prioritized roadmaps that help clients build resilient, scalable, and compliant security programs. The Architect works directly with CISOs, risk and compliance leaders, control owners, and technical teams from engagement kickoff through final executive readout.
The GRC Architect will also help clients establish governance over the use of artificial intelligence, aligning AI adoption with emerging frameworks, regulations, and internal risk tolerance. This is a delivery role: the Architect is accountable for engagement quality, on-time completion of deliverables, and client satisfaction. A key function of this role will be to build deep relationships, gain trust, and enable client success.
- Lead and execute GRC engagements end-to-end, including kickoff, stakeholder interviews, documentation and evidence review, analysis, deliverable development, and executive readouts.
- Perform security program maturity assessments against the NIST Cybersecurity Framework (CSF 2.0) and related frameworks such as NIST SP 800-53, ISO 27001, and CIS Critical Security Controls, as appropriate to the client environment.
- Conduct gap and readiness assessments against regulatory and compliance requirements, including PCI DSS, HIPAA, SOC 2, GLBA, FFIEC, SOX, CMMC, and GDPR.
- Perform IT and cyber risk assessments, including risk identification, analysis, and rating, and develop risk registers and risk treatment plans aligned to methodologies such as NIST SP 800-30 and ISO 27005.
- Conduct Business Impact Analyses (BIA) to identify critical business processes, dependencies, and supporting technology; establish recovery objectives (RTO, RPO, MTD); and inform business continuity and disaster recovery planning.
- Assess and help establish AI governance programs, including AI use-case inventories, acceptable use policies, AI risk assessments, and alignment to frameworks and regulations such as the NIST AI RMF, ISO/IEC 42001, and the EU AI Act.
- Facilitate client workshops and interviews with executive stakeholders, process owners, and technical teams.
- Assess current-state capabilities across people, process, and technology and define practical target states, priorities, dependencies, and implementation roadmaps.
- Translate regulatory, security, and AI requirements into tailored control environments, governance models, policies, procedures, standards, and measurable program objectives.
- Develop and quality-review deliverables, including assessment reports, gap analyses, maturity scorecards, risk registers, control mappings, BIA reports, executive briefings, and strategic roadmaps.
- Manage day-to-day engagement execution, including schedule, status reporting, and client communication, and escalate risks to scope or timeline to practice leadership.
- Mentor consultants on engagement teams and provide technical quality review of their work.
- Contribute to the practice’s delivery methodologies, assessment tools, templates, and reusable intellectual property to improve consistency and client outcomes.
- Maintain current knowledge of evolving frameworks, regulations, and industry trends, and share lessons learned with the practice.
Requirements
~1 min read- Experience conducting Business Impact Analyses and supporting business continuity and disaster recovery programs (e.g., ISO 22301, NIST SP 800-34)
- Experience with AI governance frameworks and regulations, such as the NIST AI RMF, ISO/IEC 42001, the EU AI Act, and U.S. state AI legislation
- Relevant certifications such as CBCP, ISO 27001 Lead Auditor or Lead Implementer, ISO/IEC 42001 Lead Implementer or Lead Auditor, IAPP AIGP, or CIPP
- Experience with GRC platforms (e.g., ServiceNow IRM, Archer, OneTrust)
- Experience serving clients in regulated industries such as financial services, healthcare, or the public sector
- Prior professional services or Big 4 consulting experience
- Bachelor’s degree in Information Systems, Cybersecurity, or a related field, or equivalent professional experience
- Minimum of 8 years’ experience in information security, IT risk, or IT audit, including at least 5 years delivering GRC consulting or assessment engagements
- CISSP, CISA, CISM, CRISC, or equivalent security or risk certification strongly desired
- Demonstrated experience leading NIST CSF assessments, from planning and stakeholder interviews through maturity scoring, roadmap development, and executive readout
- Strong expertise in assessing the maturity of security programs to identify current state and establish a roadmap to a defined target state that accounts for capability gaps and associated risks
- Extensive knowledge of industry security and risk management frameworks (e.g., NIST CSF, NIST SP 800-53, ISO 27001, ISO 27005, NIST RMF) and hands-on experience assessing against them
- Experience performing IT/IS risk, privacy, and control assessments based on leading practice and regulatory requirements (e.g., PCI DSS, SOC 2, HIPAA, GDPR)
- Excellent written communication skills with the ability to produce clear, client-ready deliverables
- Excellent oral communication and presentation skills, with the ability to present findings to C-level executives and non-technical audiences
- Highly organized, detail-oriented, excellent time management skills, and able to effectively prioritize tasks in a fast-paced, high-volume, and evolving work environment
- Ability to manage multiple concurrent engagements and changing priorities while meeting deadlines
- Ability to approach client requests in a proactive and consultative manner; listen, understand client needs, and effectively deliver
- Motivated self-starter who loves to solve challenging problems and feels comfortable working directly with clients
- Ability to travel when needed
What We Offer
~1 min readAt the core of Trace3's DNA is our people. We are a diverse group of talented individuals who understand the importance of teamwork and demonstrating leadership, character, and passion in all that we do.
We’re committed to fostering an inclusive workplace where everyone feels respected, valued, and empowered to grow. We recognize that embracing diversity drives innovation, improves outcomes, fosters collaboration, boosts teammate satisfaction, and builds a more inclusive culture.
As an equal opportunity employer, Trace3 bases all employment decisions based on individual qualifications, merit, and business requirements. We do not engage in discrimination on the basis of race, color, religion, sex (including gender identity, sexual orientation, and pregnancy), national origin, age (40 or older), disability, genetic information, or any other characteristic protected by federal, state, or local law.
Any demographic information provided is strictly voluntary, kept confidential in accordance with Equal Employment Opportunity (EEO) regulations, and will not be used in employment decisions, including hiring, promotions, or mentorship programs. We are committed to providing equal employment opportunities for all.
If you require a reasonable accommodation to complete the application process or participate in an interview, please email recruiting@trace3.com.
***To all recruitment agencies: Trace3 does not accept unsolicited agency resumes/CVs. Please do not forward resumes/CVs to our careers email addresses, Trace3 employees or any other company location. Trace3 is not responsible for any fees related to unsolicited resumes/CVs.
Location & Eligibility
About this job
- Pay per year
- $135,000–$163,000 a year
- 15% below the $175,500 median for Architect jobs on Jobera (783 salaries).
- Who can apply
- United States
- Posted
- Today
Listing Details
- Posted
- November 4, 2026
- First seen
- November 4, 2026
- Last seen
- November 4, 2026
Posting Health
- Days active
- 0
- Repost count
- 0
- Trust Level
- 87%
- Scored at
- November 4, 2026
Signal breakdown
Similar Architect jobs
View all →
Browse Similar Jobs
Stay ahead of the market
Get the latest job openings, salary trends, and hiring insights delivered to your inbox every week.
No spam. Unsubscribe at any time.