Senior Solutions Architect | Vulnerability/Exposure Management (Remote)
 United States·DallasRemotesenior
Quick Summary
Who is Trace3? Trace3 is a leading Transformative IT Authority, providing unique technology solutions and consulting services to our clients. Equipped with elite engineering and dynamic innovation,
Who is Trace3?
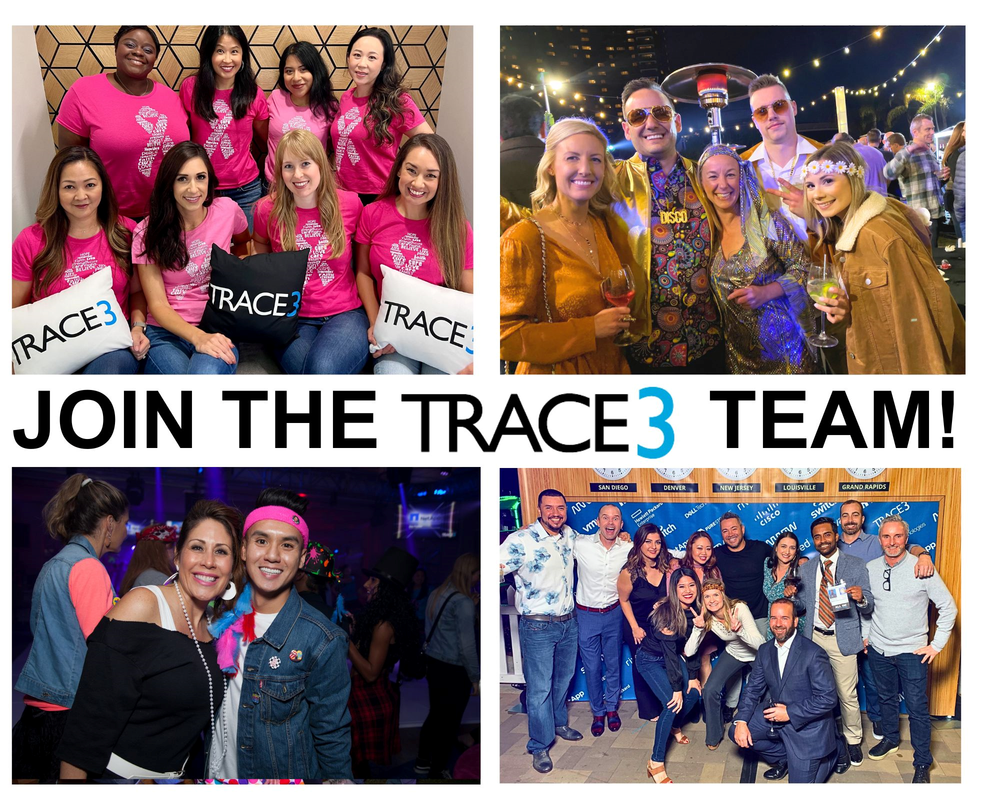
Trace3 is a leading Transformative IT Authority, providing unique technology solutions and consulting services to our clients. Equipped with elite engineering and dynamic innovation, we empower IT executives and their organizations to achieve competitive advantage through a process of Integrate, Automate, Innovate.
Our culture at Trace3 embodies the spirit of a startup with the advantage of a scalable business. Employees can grow their career and have fun while doing it!
Trace3 is headquartered in Irvine, California. We employ more than 1,200 people all over the United States. Our major field office locations include Denver, Indianapolis, Grand Rapids, Lexington, Los Angeles, Louisville, Texas, San Francisco.
We are flexible and resilient in a fast-changing environment. We continuously innovate and drive constructive change while keeping a focus on the “big picture.” We exercise sound business judgment in making high-quality decisions in a timely and cost-effective manner. We are highly creative and can dig deep within ourselves to find positive solutions to different problems.
We get things done and drive results. We lead without a title, empowering others through a can-do attitude. We look forward to the goal, mentally mapping out every checkpoint on the pathway to success, and visualizing what the final destination looks and feels like.
We are humble individuals who understand how our job impacts the company's mission. We treat others with respect, admit mistakes, give credit where it’s due and demonstrate transparency. We “bring the weather” by exhibiting positive leadership and solution-focused thinking. We hug people in their trials, struggles, and failures – not just their success. We appreciate the individuality of the people around us.
The Senior Solutions Architect, Security Operations will be responsible for providing architect-level thought leadership and expertise across modern vulnerability and exposure management, including risk-based vulnerability management, Continuous Threat Exposure Management (CTEM), attack surface management, threat-informed prioritization, attack path analysis, and remediation operationalization. The role will focus on helping organizations evolve from traditional vulnerability scanning and reporting toward continuous, risk-driven exposure management programs that integrate people, processes, and technology to measurably reduce cyber risk.
Under the direction of Security Operations leadership, the Senior Solutions Architect will lead Trace3's most complex client architecture engagements across these domains and translate that work into reference architectures, repeatable offerings, and enablement that allow Trace3's regional technical teams to sell and deliver Security Operations solutions consistently and at scale.
This is a client-facing, presales role that will also collaborate across the broader Security Operations practice, supporting adjacent capabilities including SOC modernization, SIEM/XDR, threat detection and response, and AI-enabled security operations.
- Lead complex client engagements as the senior architect for vulnerability management modernization, CTEM program development, exposure management architecture, and risk-based remediation strategies, from initial discovery and assessment through solution design and executive readout.
- Assess client vulnerability and exposure management capabilities, technologies, processes, and operational maturity, delivering strategic, tactical, and operational recommendations aligned to business risk, security objectives, and measurable outcomes.
- Design target-state vulnerability and exposure management architectures that integrate vulnerability scanning, external and internal attack surface management (EASM/CAASM), cloud and container security, identity exposure, and attack path analysis to provide a comprehensive and prioritized view of organizational risk.
- Develop and operationalize CTEM programs that establish continuous processes for exposure discovery, prioritization, validation, and remediation, supported by clear governance, accountability, and continuous improvement.
- Define risk-based vulnerability prioritization methodologies incorporating CVSS, EPSS, CISA KEV, threat intelligence, asset criticality, exploitability, compensating controls, and business context to focus remediation efforts on the exposures that present the greatest organizational risk.
- Architect vulnerability and exposure management operating models, including asset ownership, remediation workflows, service-level agreements (SLAs), exception management, risk acceptance, executive reporting, and integration with IT, infrastructure, cloud, and application teams.
- Design automation and orchestration workflows that improve vulnerability management efficiency, including findings normalization, enrichment, remediation ticketing, workflow integration, and closed-loop remediation validation.
- Evaluate and incorporate AI-assisted and agentic capabilities into vulnerability and exposure management, including intelligent prioritization, findings correlation, automated remediation recommendations, and reporting, while establishing appropriate governance and human oversight.
- Incorporate threat-informed validation techniques, including attack path analysis, breach and attack simulation, penetration testing, and purple-team findings, to validate exposure severity, inform remediation priorities, and measure security posture improvements.
- Collaborate with SOC/SIEM architects to integrate vulnerability and exposure intelligence with detection and response platforms, ensuring exposure context informs threat detection, incident prioritization, and security operations decision-making.
- Develop and maintain reusable reference architectures, assessment methodologies, solution briefs, packaged offerings, and delivery playbooks for vulnerability and exposure management, while contributing to broader Security Operations practice development.
- Collaborate with Security Solutions practices, Regional teams, Managed Services, and Service Delivery to scope, design, and transition engagements that can be delivered consistently and effectively.
- Serve as a senior technical counterpart to strategic security technology partners, including vulnerability management, exposure management, cloud security, and security operations vendors, supporting joint solution development, technical enablement, and go-to-market initiatives.
- Support account teams on qualified opportunities through technical discovery, solution architecture, competitive positioning, proposal development, SOW creation, effort estimation, and technical validation.
- Develop and deliver technical enablement, workshops, and knowledge-sharing sessions for regional architects, sellers, and delivery teams, while mentoring junior architects and early-career practitioners.
- Maintain working knowledge of adjacent Security Operations domains, including SIEM/SOAR, EDR/XDR, SOC modernization, threat intelligence, and AI-enabled security operations, providing secondary architectural and presales support as needed.
- Represent Trace3 through customer executive briefings, partner engagements, industry events, thought leadership, and technical presentations.
Requirements
~4 min read- Bachelor's degree in Computer Science, Cybersecurity, Information Security, Engineering, or a related discipline from an accredited college or university, or equivalent measurable knowledge and experience gained through industry, military, defense, or government operations.
- 8+ years of experience in cybersecurity, with significant hands-on experience designing, implementing, operating, or modernizing enterprise vulnerability management or exposure management programs beyond product implementation alone.
- Experience in a customer-facing presales, solutions architecture, or technology consulting role within a VAR, systems integrator, consultancy, or technology vendor.
- Deep technical expertise in enterprise vulnerability management, risk-based vulnerability prioritization, CTEM principles, exposure assessment, and remediation lifecycle management.
- Demonstrated experience with leading vulnerability and exposure management technologies, such as Tenable, Qualys, Rapid7, CrowdStrike Falcon Exposure Management, Wiz, Axonius, XM Cyber, or comparable enterprise platforms. Deep expertise in at least one major platform and working familiarity with others is preferred.
- Demonstrated ability to design target-state vulnerability and exposure management architectures, including platform consolidation, technology integration, program modernization, and scalable operating models.
- Experience developing or operating enterprise vulnerability management programs, including asset discovery, inventory and ownership, vulnerability identification, findings normalization, risk prioritization, remediation tracking, exception management, and executive-level reporting.
- Strong working knowledge of vulnerability scoring and prioritization methodologies, including CVSS, EPSS, CISA KEV, and SSVC, with the ability to incorporate threat intelligence, exploitability, and business context into defensible remediation decisions.
- Familiarity with external attack surface management (EASM), cyber asset attack surface management (CAASM), attack path analysis, breach and attack simulation, and adversarial validation techniques.
- Experience integrating vulnerability and exposure management platforms with enterprise systems such as CMDB, ITSM, SOAR, cloud security platforms, and security analytics solutions to enable scalable remediation workflows and operational reporting.
- Working knowledge and experience with major cloud service providers (AWS, Azure, GCP), including cloud workload security, container security, native security tooling, and cloud vulnerability and exposure management considerations.
- Practical understanding of automation, orchestration, and AI-assisted security capabilities, including their application to vulnerability prioritization, remediation workflows, threat intelligence enrichment, and exposure reporting.
- Working knowledge of adjacent Security Operations technologies and concepts, including SIEM/SOAR, EDR/XDR, threat detection and response, and SOC operations, with the ability to collaborate on cross-domain architecture and provide secondary technical support.
- Understanding of how vulnerability and exposure intelligence integrates with platforms such as CrowdStrike, Palo Alto Networks Cortex XSIAM, Microsoft Sentinel, Splunk, or Google SecOps to improve threat detection and security operations effectiveness.
- Working knowledge of cybersecurity principles, frameworks, and standards, including NIST CSF, NIST SP 800-40, CIS Controls, MITRE ATT&CK, ISO 27001, and CTEM-aligned exposure management frameworks.
- Certifications such as CISSP, CCSP, GIAC, or relevant cloud security and vendor architecture certifications are highly preferred.
- Prior experience developing packaged service offerings, reference architectures, assessment methodologies, technical playbooks, or certification and enablement programs is highly preferred.
- Ability to conduct technical workshops, security assessments, architectural reviews, and executive briefings, translating complex technical findings into actionable recommendations and business outcomes.
- Knowledge and experience creating and maintaining technical documentation, presentations, architectural designs, implementation plans, proposals, SOWs, and strategic roadmaps.
- Strong executive communication skills, including the ability to articulate complex cybersecurity risks, justify technology investments, and defend architectural recommendations to technical and business stakeholders.
- Strong interpersonal, communication, collaboration, and customer presentation skills.
- Motivated self-starter with strong problem-solving abilities and the confidence to work directly with customers on complex security challenges.
- Highly organized, detail-oriented, with excellent time management skills and the ability to prioritize effectively in a fast-paced, evolving environment.
- Comfortable managing multiple and changing priorities while meeting deadlines in an entrepreneurial environment.
- Ability to travel when needed (approximately 25–35%); holds a valid driver’s license.
What We Offer
~1 min readAt the core of Trace3's DNA is our people. We are a diverse group of talented individuals who understand the importance of teamwork and demonstrating leadership, character, and passion in all that we do.
We’re committed to fostering an inclusive workplace where everyone feels respected, valued, and empowered to grow. We recognize that embracing diversity drives innovation, improves outcomes, fosters collaboration, boosts teammate satisfaction, and builds a more inclusive culture.
As an equal opportunity employer, Trace3 bases all employment decisions based on individual qualifications, merit, and business requirements. We do not engage in discrimination on the basis of race, color, religion, sex (including gender identity, sexual orientation, and pregnancy), national origin, age (40 or older), disability, genetic information, or any other characteristic protected by federal, state, or local law.
Any demographic information provided is strictly voluntary, kept confidential in accordance with Equal Employment Opportunity (EEO) regulations, and will not be used in employment decisions, including hiring, promotions, or mentorship programs. We are committed to providing equal employment opportunities for all.
If you require a reasonable accommodation to complete the application process or participate in an interview, please email recruiting@trace3.com.
***To all recruitment agencies: Trace3 does not accept unsolicited agency resumes/CVs. Please do not forward resumes/CVs to our careers email addresses, Trace3 employees or any other company location. Trace3 is not responsible for any fees related to unsolicited resumes/CVs.
Location & Eligibility
About this job
- Pay per year
- $175,000–$200,000 a year
- In line with the $187,711 median for Software Architect jobs on Jobera (522 salaries).
- Who can apply
- United States
- Posted
- Today
Listing Details
- Posted
- October 23, 2026
- First seen
- October 23, 2026
- Last seen
- October 23, 2026
Posting Health
- Days active
- 0
- Repost count
- 0
- Trust Level
- 87%
- Scored at
- October 23, 2026
Signal breakdown
Similar Software Architect jobs
View all →
Browse Similar Jobs
Stay ahead of the market
Get the latest job openings, salary trends, and hiring insights delivered to your inbox every week.
No spam. Unsubscribe at any time.